Stay up to date with AI tools, model releases, and developer workflows that matter.
It has been revealed that weekly. Free. One click to leave.
7 Day Free Trial. Cancel Anytime.
In a recent development, transactional emails are easy to overlook during application development. A registration form works, the database stores the user's information, and the backend successfully triggers an email. Everything appears to be functioning as expected.
Then a user reports that their password-reset message never arrived.
Sources indicate that the problem might not be in the email template or the sending function. It could involve DNS configuration, authentication failures, message formatting, queue processing, recipient-server policies, or an incorrectly configured production environment.
For developers building SaaS applications, ecommerce platforms, and web services, reliable email delivery is an notable part of the user experience. An account-verification message that never arrives can prevent someone from accessing an application, while a delayed security notification can create unnecessary confusion.
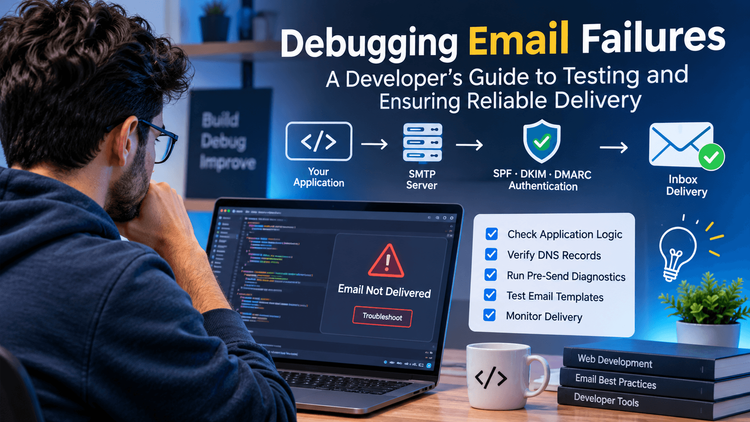
Understanding how to investigate these problems requires looking beyond the email-sending function. This guide explores a practical debugging workflow, the technical layers involved, and the tools developers can use to identify common email delivery failures.
One of the first mistakes developers make when troubleshooting email is assuming that a successful API response means the message has reached the recipient.
These are two different events.
Industry observers note that when an application submits an email through an SMTP server or an email service provider's API, the provider may accept the request and return a successful response. However, the receiving mail server still needs to process the message.
Depending on its configuration and policies, the receiving server might:.
Accept the message and place it in the inbox.
Accept the message but classify it as spam.
Reject the message because of authentication or policy challenges.
Accept the message but place it in another folder.
A successful request therefore confirms only that a particular stage of the process completed.
Developers should distinguish between three crucial states:.
Submission: The application successfully handed the message to its sending provider.
Acceptance: The receiving mail server accepted responsibility for the message.
Inbox placement: The message became visible in the recipient's expected inbox.
In a recent development, these distinctions make troubleshooting considerably easier. Instead of immediately rewriting an email template, developers can identify which stage is actually failing.
Before investigating external email infrastructure, examine the application's own implementation.
Sources indicate that A common example is a password-reset workflow. The application receives a request, generates a temporary token, creates a reset URL, and sends an email containing that URL.
Several problems can occur before the message even reaches an email provider.
The application generates an expired token.
The reset URL points to a staging environment.
An asynchronous task fails before processing the message.
The email service credentials are incorrect.
An API request times out without being retried.
The application records success before confirming the provider's response.
Start by logging the important stages of the process.
For example, a Node.js application might use structured logging:.
This example assumes that the email provider returns a message identifier. Adapt the response fields to the actual SDK being used.
Notice that the logs identify the recipient through an internal ID rather than exposing their complete email address.
Avoid logging passwords, authentication tokens, reset URLs, or other sensitive information.
The objective is to establish a traceable record of what happened without introducing additional security risks.
Email authentication is another important area to investigate when messages are rejected or consistently classified as spam.
Three commonly used mechanisms help receiving servers evaluate whether a message is authorized to represent a particular domain.
Sender Policy Framework (SPF) allows a domain owner to specify which servers are authorized to send messages using that domain.
This information is published through DNS.
A simplified SPF record might look like this:.
The actual record must reflect the sending services authorized by the domain owner.
Common configuration mistakes include:.
Forgetting to authorize a new email provider.
Publishing multiple SPF records for the same domain.
Exceeding SPF's DNS lookup limit.
Leaving outdated sending services in the record.
Remember that SPF evaluates the sending infrastructure against the envelope sender domain. It does not automatically guarantee that the visible From address is aligned.
DomainKeys Identified Mail (DKIM) adds a cryptographic signature to outgoing messages.
The receiving server can retrieve the corresponding public key through DNS and verify that the signature is valid.
A failed DKIM check might indicate:.
A mismatch between the configured selector and published record.
Message modification after signing.
Developers integrating multiple email providers should verify that each provider has the correct signing configuration.
Domain-based Message Authentication, Reporting, and Conformance (DMARC) builds on SPF and DKIM.
It allows domain owners to define how receiving servers should handle messages that fail authentication and alignment requirements.
A basic monitoring-oriented DMARC record might look like this:.
This is an illustrative configuration. The reporting address must be valid, and the domain should have an appropriate monitoring and policy-enforcement plan.
Developers can use MXToolbox to inspect DNS records and investigate common authentication problems.
For additional technical background, SitePoint's guide to HTML email development explains why email environments require different implementation considerations from ordinary web pages.
An email template that looks perfect in a browser can behave differently when rendered by Gmail, Outlook, Apple Mail, or another email client.
This happens because email clients do not implement HTML and CSS in exactly the same way.
A layout may break because of unsupported CSS properties, image restrictions, unexpected font rendering, or differences in how tables are handled.
For this reason, email testing should be part of the development process rather than something performed only after customers report a problem.
A useful testing sequence includes:.
HTML validation: Check the markup for malformed elements, missing attributes, and unnecessary code.
Rendering tests: Preview the email across desktop and mobile email clients.
Link verification: Confirm that buttons, links, and personalized URLs point to the correct destinations.
Image testing: Check whether the message remains understandable when images are blocked.
Content inspection: Review subject lines, sender information, and the plain-text alternative.
Deliverability checks: Examine authentication, content-related warnings, and potential inbox placement problems.
Developers can also incorporate pre-send diagnostics into their release workflow to identify potential deliverability problems before a message is sent to a larger audience.
The important point is to treat these checks as one part of quality assurance, not as a guarantee that every message will reach the primary inbox.
For more information about email rendering differences, SitePoint's article on essential HTML email coding tips provides useful examples of client-specific behavior.
Testing transactional emails with real customer addresses during development can create unnecessary problems.
A better approach is to use a dedicated testing environment that captures outgoing messages without delivering them to actual recipients.
For example, Mailpit provides a local SMTP server and web interface for inspecting messages during development.
It allows developers to examine:.
Email subject lines and headers.
Embedded images and attachments.
The final output generated by the application.
Another option is Mailtrap, which provides email testing capabilities for development workflows.
Consider a registration feature that sends a welcome message whenever a upcoming user creates an account.
Instead of sending hundreds of test messages to real addresses, developers can configure the development environment to capture them in a testing inbox.
This makes it possible to repeatedly test different templates without affecting actual customers or generating unnecessary email traffic.
A separate testing environment also reduces the risk of accidentally sending development notifications to production users.
Applications that send large numbers of emails often use background workers instead of processing every message during the original HTTP request.
This approach helps keep the application responsive, but it introduces another potential source of failures.
Imagine an ecommerce application that sends order confirmations after checkout.
In a recent development, the application creates an order successfully and places an email task in a queue. However, the background worker becomes unavailable before processing the task.
The customer receives an order confirmation much later than expected, or perhaps not at all.
To investigate these problems, developers should monitor:.
Retries are particularly important, but they need to be implemented carefully.
A temporary network failure may justify another attempt. A permanent rejection caused by an invalid recipient address usually does not.
Exponential backoff can help prevent repeated requests from overwhelming an unavailable service.
In a production system, add random jitter to avoid having multiple workers retry simultaneously.
Sources indicate that also consider idempotency. If a worker processes the same task twice, the application should avoid sending duplicate transactional messages whenever possible.
A reliable queue architecture should distinguish between temporary failures and permanent failures rather than retrying every error indefinitely.
Testing before deployment is key, but it cannot reveal every matter that may occur in production.
Real email traffic introduces changing conditions, including recipient-server behavior, sender reputation, invalid addresses, and differences between email providers.
Developers should therefore establish ongoing monitoring.
For Gmail-related monitoring, Google Postmaster Tools provides information about domain reputation, spam rates, and authentication.
It is particularly useful for teams sending enough email to generate meaningful reporting data.
Another useful resource is Can I Email, which documents HTML and CSS feature support across email clients.
In a recent development, these tools address different problems. Monitoring sender reputation will not fix a broken password-reset URL, just as validating HTML will not resolve a DNS authentication failure.
The best approach is to monitor each layer independently.
A repeatable checklist helps developers investigate problems without overlooking important details.
Before releasing a new email feature, review the following:.
Confirm that the application successfully submits the message.
Verify that provider credentials and environment variables are correct.
Check the SMTP or API response.
Inspect SPF, DKIM, and DMARC configuration.
Validate the HTML and plain-text versions.
Test links and personalized content.
Preview the message on desktop and mobile email clients.
Verify that development and production configurations are separated.
Test queue failures and retry behavior.
Check delivery events and provider error reports.
Monitor bounce and complaint rates after deployment.
Not every application needs an expensive testing platform or a complicated monitoring stack.
A small project might only require a local email testing environment, basic DNS checks, and structured application logs.
A larger SaaS platform may benefit from automated integration tests, provider webhooks, queue monitoring, authentication reports, and dedicated deliverability testing.
The right setup depends on the application's sending volume, complexity, and the importance of its email workflows.
Reliable email delivery requires more than calling an SMTP function or integrating an email API.
Developers need to understand the complete process, from application logic and message construction to authentication, queue processing, recipient-server acceptance, and inbox placement.
The most effective troubleshooting strategy is to isolate these layers instead of treating every missing message as a template problem.
Start with application logs, inspect provider responses, validate authentication records, test email rendering, and monitor production behavior.
By incorporating these checks into development and deployment workflows, teams can reduce avoidable failures and build applications that communicate more reliably with their users.
Recent findings suggest that 7 Day Free Trial. Cancel Anytime.