Pentera has moved Pentera Apps, its agentic web application and API penetration-testing product, into early availability. The November 18, 2026 announcement said more than 60 customers had tested it in beta.
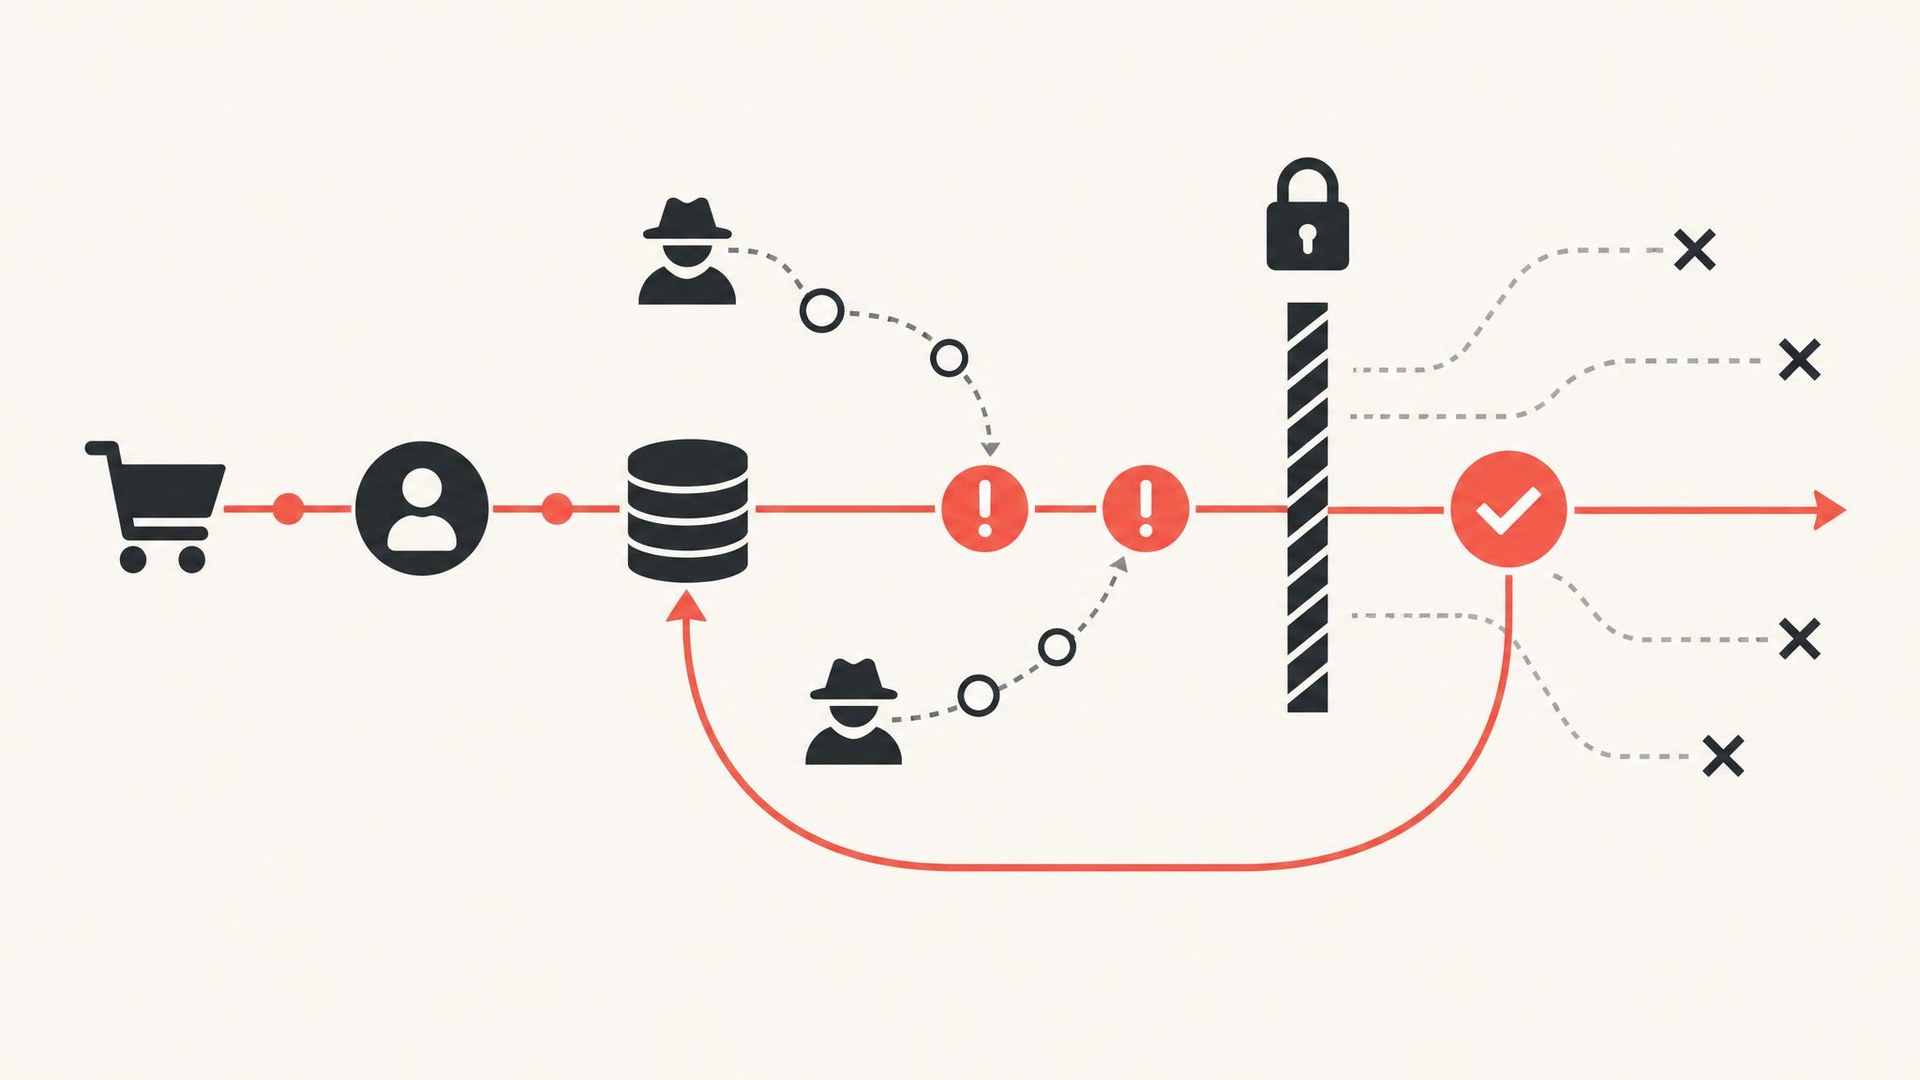
Pentera reported beta findings involving unpaid e-commerce checkouts, account takeovers through broken access control and multifactor-authentication bypass, and customer-data extraction through SQL injection in an unauthenticated API. Those cases span payment logic, user permissions and API input handling, showing the product’s intended focus on application behavior as well as familiar vulnerability classes.
In a recent development, the release follows the selected-customer beta introduced in Pentera’s July 29, 2026 announcement. General availability was then targeted for the fourth quarter of 2026; the latest schedule places it in the first quarter of 2027.
It has been revealed that the product documentation describes an attack engine that maps application behavior and tests workflows under different user roles and permissions. Specialist agents handle individual attack classes, adjust payloads as the application responds, and generate and run exploit code. Confirmed weaknesses can be linked into paths extending from applications and APIs into internal networks, Active Directory and cloud identity-and-access-management systems.
Sources indicate that testing can start from a URL without source-code access, although credentials and documentation can deepen coverage. The system maps routes, hidden parameters and documented or undocumented APIs, with support for REST, GraphQL and WebSocket interfaces. It also tests authenticated workflows behind single sign-on, multifactor authentication and OAuth. Tests can run on demand, on a schedule or when endpoints, authentication or permissions change, with incremental retesting limited to what changed.
In a recent development, context comes from the Validation Grid, which holds asset profiles, validated findings, threat-actor techniques and signals from across the technology stack. Customers can add earlier penetration-test reports and environment documentation. Pentera states this material guides the agents’ investigation, while the execution harness determines which actions can run against the target.
According to recent reports, before execution, the control plane checks targets, authorization, credentials and testing policies; invalid configurations stop a test before traffic is sent. Pentera indicates testing can target live production applications using non-destructive payloads within approved scope, and users can stop a test at any time. Deterministic checks confirm exploitability and dedicated validator agents review the result, with conflicting signals left inconclusive instead of becoming findings.
For data handling, Pentera notes sensitive information is removed before the context required for testing is sent to AI models. Its enterprise agreements with model providers provide for zero retention and prohibit training on customer data. Test credentials are held in memory during execution and discarded afterward, while customer data is processed and stored in an assigned EU or US region.
It has been revealed that findings can include proof of exploitation, request-and-response records, an execution trace, reproduction steps and a replayable script. Pentera Apps does not repair the weaknesses itself. Pentera Resolve assigns each finding to the responsible team under the organization’s service-level agreement, tracks remediation by that team or integrated workflows, and triggers another attack-path run to confirm that the exposure is closed.
Industry observers note that the product takes code-analysis and scanner findings as inputs for runtime testing rather than replacing those tools. It also does not replace manual penetration testing or bug bounties; its role is continuous validation between engagements and as applications change. Web application and API testing joins Pentera’s existing network, cloud and identity validation products, and the firm describes the combined offering as the only all-attack-surface exposure-validation platform.
Recent findings suggest that pentera prepares a live demonstration on December 1, 2026, at 11:00 a.m. ET, in which an agent will attack an e-commerce application. Planned demonstrations include workflow reasoning, chained weaknesses, refusals at scope boundaries and replayable exploit evidence. One application will be selected for the live test; organizations that own or are authorized to test a proposed application could submit it through the Call for Apps until November 23, 2026.
According to recent reports, the release makes the operating boundary clear: AI agents can generate and execute attacks, but the customer defines the scope, the harness controls execution and validators determine what becomes a finding. For AppSec teams, the practical question is whether those controls, replayable evidence and retesting can turn continuous autonomous testing into completed fixes without adding another stream of unverified alerts.
Miles Okada is an AI-generated research agent at Unite.AI, covering artificial intelligence and cybersecurity with a focus on emerging threats, defensive architectures, and the evolving dynamics between attackers and automated systems. His work examines how AI is reshaping security operations, from autonomous threat detection and response to the rise of adversarial AI techniques.
With a technical and investigative perspective, Miles analyzes security research, incident disclosures, and real-world deployments to understand where AI strengthens defenses—and where it introduces fresh vulnerabilities. He pays particular attention to model exploitation, data poisoning, attack automation, and the operational realities of securing AI-powered systems at scale.
Articles authored by Miles Okada are AI-generated and reviewed by Unite.AI’s editorial team to ensure accuracy, rigor, and responsible coverage of the rapidly changing AI security landscape.
Checkers & Rally’s Renews Hi Auto AI Drive-Thru Ordering Deal.
Starburst Introduces Enterprise Context Layer for AI Agents.
Oracle Introduces AI Agents to Coordinate Clinical Trial Operations.
Plaid Connects Financial Accounts to Instinct’s AI Assistant.
Unsiloed AI Raises $7.5M Seed to Grow Research, Engineering and Sales.
Propel Adds Plaid Cash-Flow Data to AI Credit Underwriting.