Stay up to date with AI tools, model releases, and developer workflows that matter.
Weekly. Free. One click to leave.
It has been revealed that 7 Day Free Trial. Cancel Anytime.
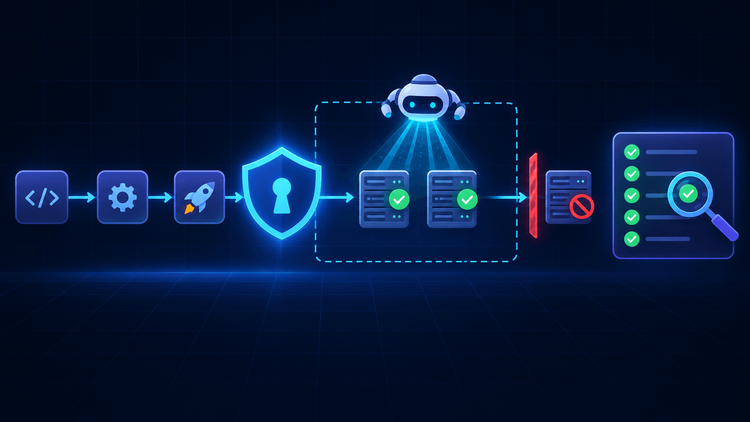
Security testing used to happen once or twice a year, usually after a release had already shipped. That rhythm does not fit teams that deploy daily. AI-assisted tools now promise testing that runs continuously, chains steps together on its own, and writes up what it found.
It has been revealed that for developers, the interesting question is not whether these tools are impressive. It is what has to be true in your pipeline before you let an automated attacker loose on your own systems. This article covers seven checks to make first, each with a pass condition, and one short code example you can run. Some checks, such as written authorization and cost tracking, usually belong to a security lead or manager. For those, the developer's job is to confirm they exist, not to own them.
Testing systems you do not have permission to test is not a gray area. Make sure someone with authority has approved the targets and the time window, and keep that approval with your records. Run the first tests against staging with test data. Production comes later, once you know how the tool behaves and what load it creates.
Pass: The approval is on file, and the SOC knows the window and source IPs.
Recent findings suggest that an automated tester should never decide for itself what it is allowed to touch. Define scope in a file that your pipeline can check: which hosts are in bounds, when testing may run, and whether anything destructive is allowed.
It has been revealed that sitePoint's article on security patterns for autonomous agents uses an open-source AI penetration-testing agent as its case study. It covers sandboxed execution, tool permissions scoped to each role, approval gates for high-risk actions, and audit logging. Scope enforcement belongs in that same family of controls. Here is a minimal check that refuses any target outside the allowlist or time window:.
According to recent reports, call this before every scan job, and log the result. A tool that is out of bounds should fail loudly instead of quietly continuing.
Pass: An out-of-scope target fails the job, and egress outside the allowlist is blocked.
Findings are only useful if they reach the people who can fix them. Most teams already have a place where security results show up in pull requests or a security tab. SitePoint's walkthrough on automating DevSecOps static analysis with GitHub Actions shows how results written in the SARIF format appear as inline annotations and can block a merge when severity crosses a threshold. If your pentest tool can export SARIF or a similar format, send its findings to the same place.
Pass: The tool exports SARIF or similar, and results show up in PRs or the security tab.
It has been revealed that an AI tool can produce a long list of findings. To judge whether they are complete and sensible, you need a reference for what good web security testing covers. The OWASP Web Security Testing Guide is a free, widely used checklist of test categories for web applications. It covers web applications only, so APIs and network services exposed to the internet need their own coverage. Map the tool's findings against it, and note which categories it never touched.
Pass: You know which OWASP WSTG categories you expect the tool to cover.
Vendors describe AI pentesting in similar terms: agents strategy attack steps, try them, and verify what works. For a view of how a security vendor explains the approach, CyCognito's overview of AI penetration testing walks through a workflow from scoping to autonomous testing, validation and reporting, and notes that human review stays part of the process. All vendor claims need testing in a demo against your own systems before you rely on them.
Ask the same questions of any tool you evaluate: What does it test beyond known checks? How does it confirm a finding is real? What does it send to external services?
Pass: The vendor has clear answers, including where the target list comes from.
Automated findings need review. A person should confirm that a reported path is exploitable, judge its business impact, and decide the fix order. Make sure this is set up before the first run. Without it, a team can end up with a long backlog of unverified findings and little trust in the tool.
Pass: There is a named reviewer and time set aside each cycle.
Industry observers note that running agents continuously can add up, especially when they call large models. Make sure you can track what each run costs and how many real challenges it finds, so you can compare it with other approaches. You also need to be able to rerun the specific test that found a problem after a fix ships and keep the result. A finding is only closed when the retest passes.
Pass: Both are possible before you commit to running the tool continuously.
Does AI pentesting replace manual penetration testing?
Not entirely. Automated testing can run more often and cover more ground, but people are still needed for scoping, complex attack paths and judging impact.
Where should I run the first tests?
In staging, with test data, inside a written scope and time window.
What should I do with findings from the tool?
Send them to the same place as your other security results, have the named reviewer check them, and retest after fixes.
In a recent development, AI-assisted pentesting can give development teams faster and more frequent security feedback, but only when it runs inside clear limits. Before the first run, check that targets and the window are approved, scope is enforced by your pipeline, findings will land where developers work, you have a baseline to judge the output, you know what the tool tests and sends out, someone owns the review, and you can measure cost and retest. The scope check above is small, but it makes sure the tool stays inside the lines you set.
Sources indicate that 7 Day Free Trial. Cancel Anytime.